
Two separate security crises are now hitting the web’s core infrastructure. A certificate authority issued intermediate certificates whose private keys could be guessed by anyone, and details of two critical PHP vulnerabilities leaked before patches were ready. Browser makers fixed the certificate problem within hours. The rest of the internet, including Linux servers, Docker images, and IoT devices, still waits on administrators to apply updates by hand.
Eight intermediate certificates issued by eMudhra, a certificate authority based in India, were found to have private keys weak enough to be calculated directly from the certificates. The certificates linked back to roots trusted by Chrome, Firefox, Safari, and Windows, along with many operating systems and software trust stores. Anyone who held one of the keys could have issued a valid certificate for any domain and used it to pose as that site, reading or altering its traffic.
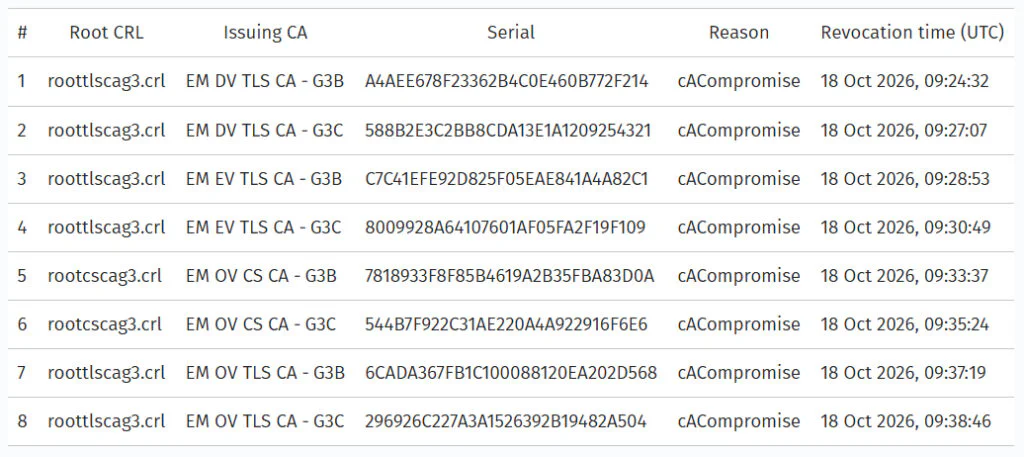
A correctly generated P-384 key has roughly 384 bits of entropy. The eMudhra keys had between 3 and 8 bits, and one was simply the number 4. All eight can be recovered by testing at most 256 values. eMudhra attributed the problem to an error in a key-generation script, whose output was then used by mistake. That puts the exposure at about 18 months, ending when a researcher reported it this month. The company says most of the certificates were never deployed and that it has found no evidence of misuse.
Browser makers moved fast. Chrome and Firefox blocked the compromised keys within hours using their remote revocation lists, so users didn’t need to update or restart anything. Apple and Microsoft followed suit by October 20.
The larger issue is software that isn’t a browser. Servers, containers, command-line tools, and embedded devices often use a static bundled list of trusted roots and don’t check revocation. Go, Python’s certifi, curl, Node.js, and most major Linux distributions have shipped fixes. Java, Bun, and FreeBSD were still pending when this was written.
Go cryptography maintainer Filippo Valsorda told Ars Technica, “This will be a massive cleanup job, bigger than Heartbleed.” An attack still depends on the attacker being positioned between a user and a server, which is straightforward on a shared network.
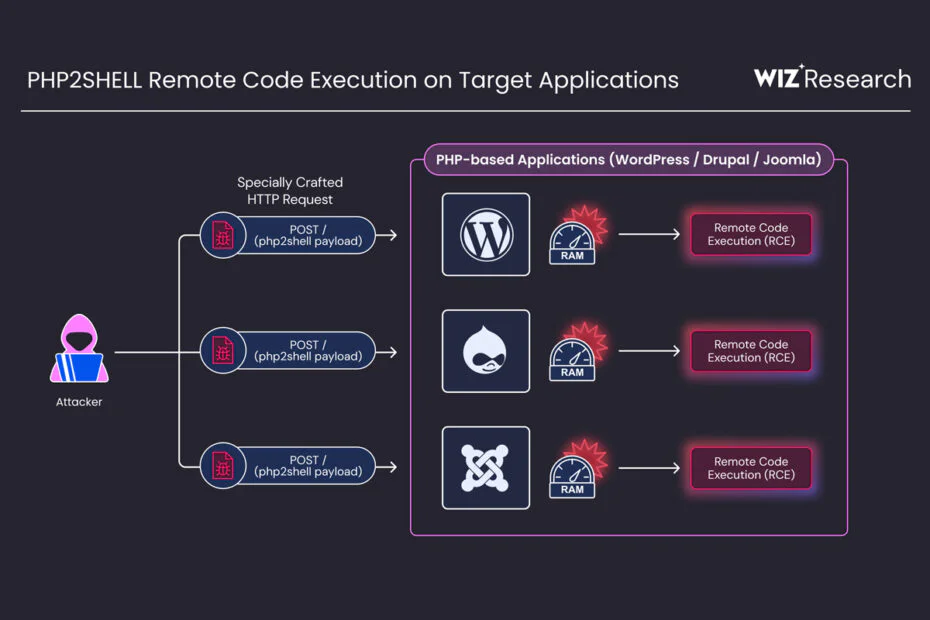
A second major emergency this week involves PHP. Because PHP powers close to 70% of websites, including WareData, the possible impact is large. Sites running WordPress, Drupal, MediaWiki, and other software are affected. The PHP team released emergency fixes for two vulnerabilities, CVE-2026-109618 and CVE-2026-109619, collectively named PHP2Shell and scored 9.2 out of 10 for severity.
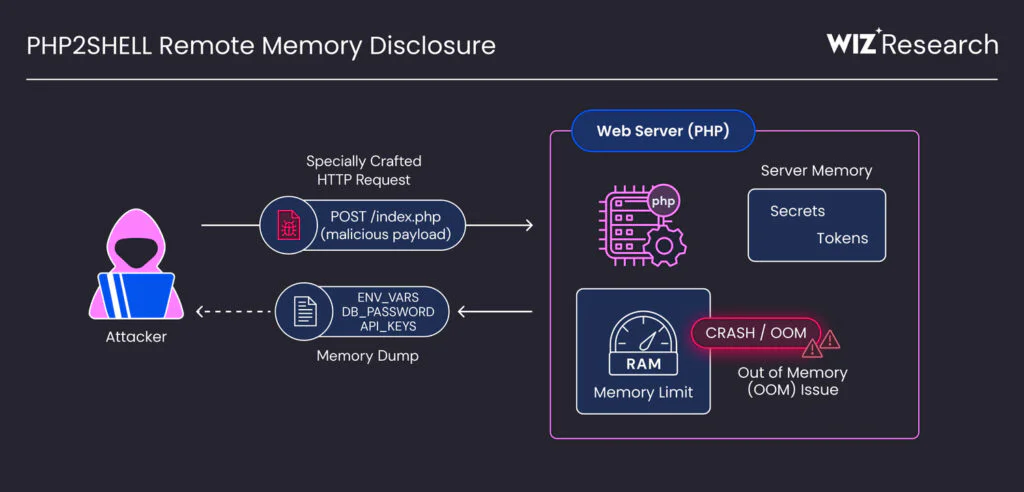
Both vulnerabilities result from PHP leaving its memory corrupted when a request terminates abnormally. An attacker can turn this into code execution or use it to read sensitive data, such as passwords and API keys, from server memory. Because the flaw is in the PHP runtime, a site is exposed regardless of how secure its own code is.
Wiz, Calif, and OpenAI discovered the flaws. Wiz says every PHP release from the past decade is affected by at least one of them, and that AI tools made it practical to build the complex exploit chain. The finding suggests that bugs once written off as too hard to exploit may no longer be safe to ignore.
PHP rushed out the fixes after details leaked on October 20, ahead of the coordinated disclosure schedule. The project patched immediately, but Cloudflare’s CTO said exploitation attempts had already begun before fixes were available.
Server administrators should update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 as soon as possible. Servers running Apache with mod_php are at the highest risk, since one unauthenticated request can trigger the attack before any application code executes. The FBI, NSA, and the UK’s National Cyber Security Centre advised organizations to patch immediately or take PHP systems offline until patching is possible.
Maybe you would like other interesting articles?